Every subscription, one secure login
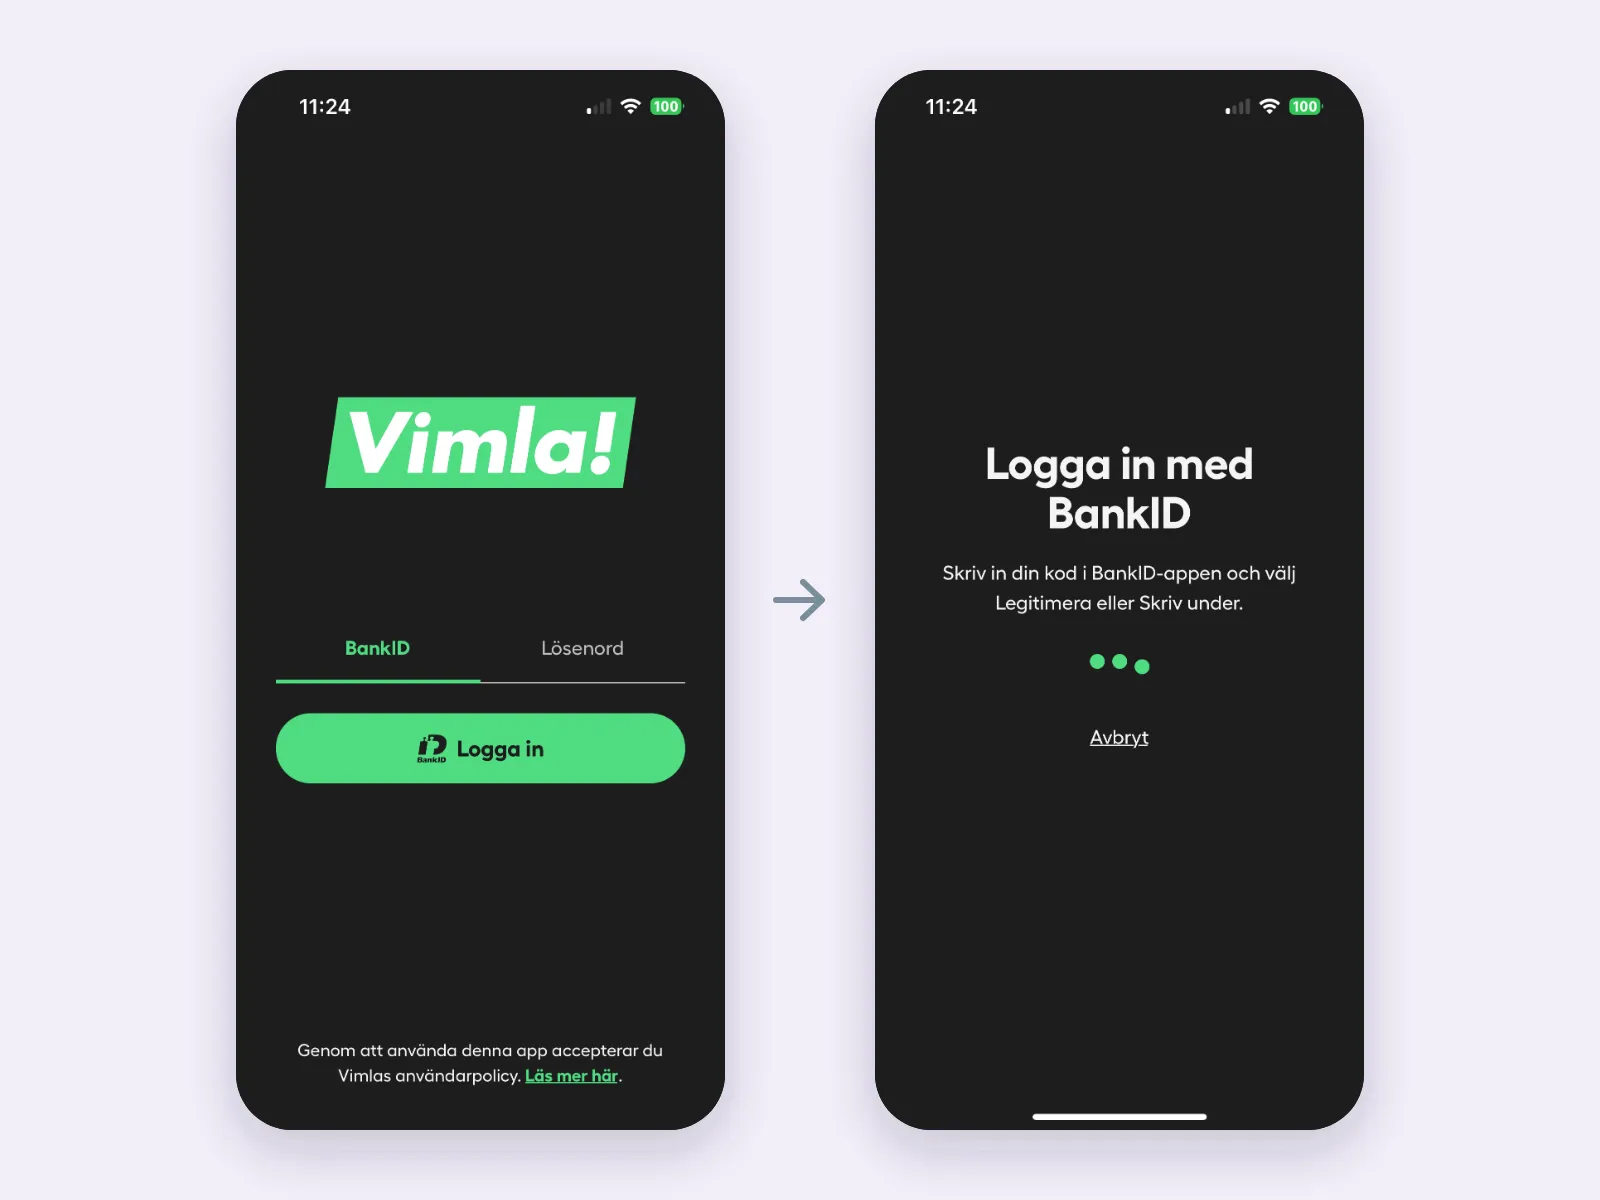
Vimla customers logged in with an email address and a password, one pair for every subscription. I designed and built the BankID login across web, mobile and backend. It was my first delivery at Vimla.
- 1 login
- for all of a customer’s subscriptions
- 2021
- shipped, and still in use today
The challenge
Customers logged in with an email address and password, with no second factor protecting their accounts. Each subscription was also tied to its own email address, so a customer with four subscriptions needed four addresses and four passwords. Vimla needed a more secure login, and one that let customers reach all their subscriptions from a single identity.
What I did
The login flows
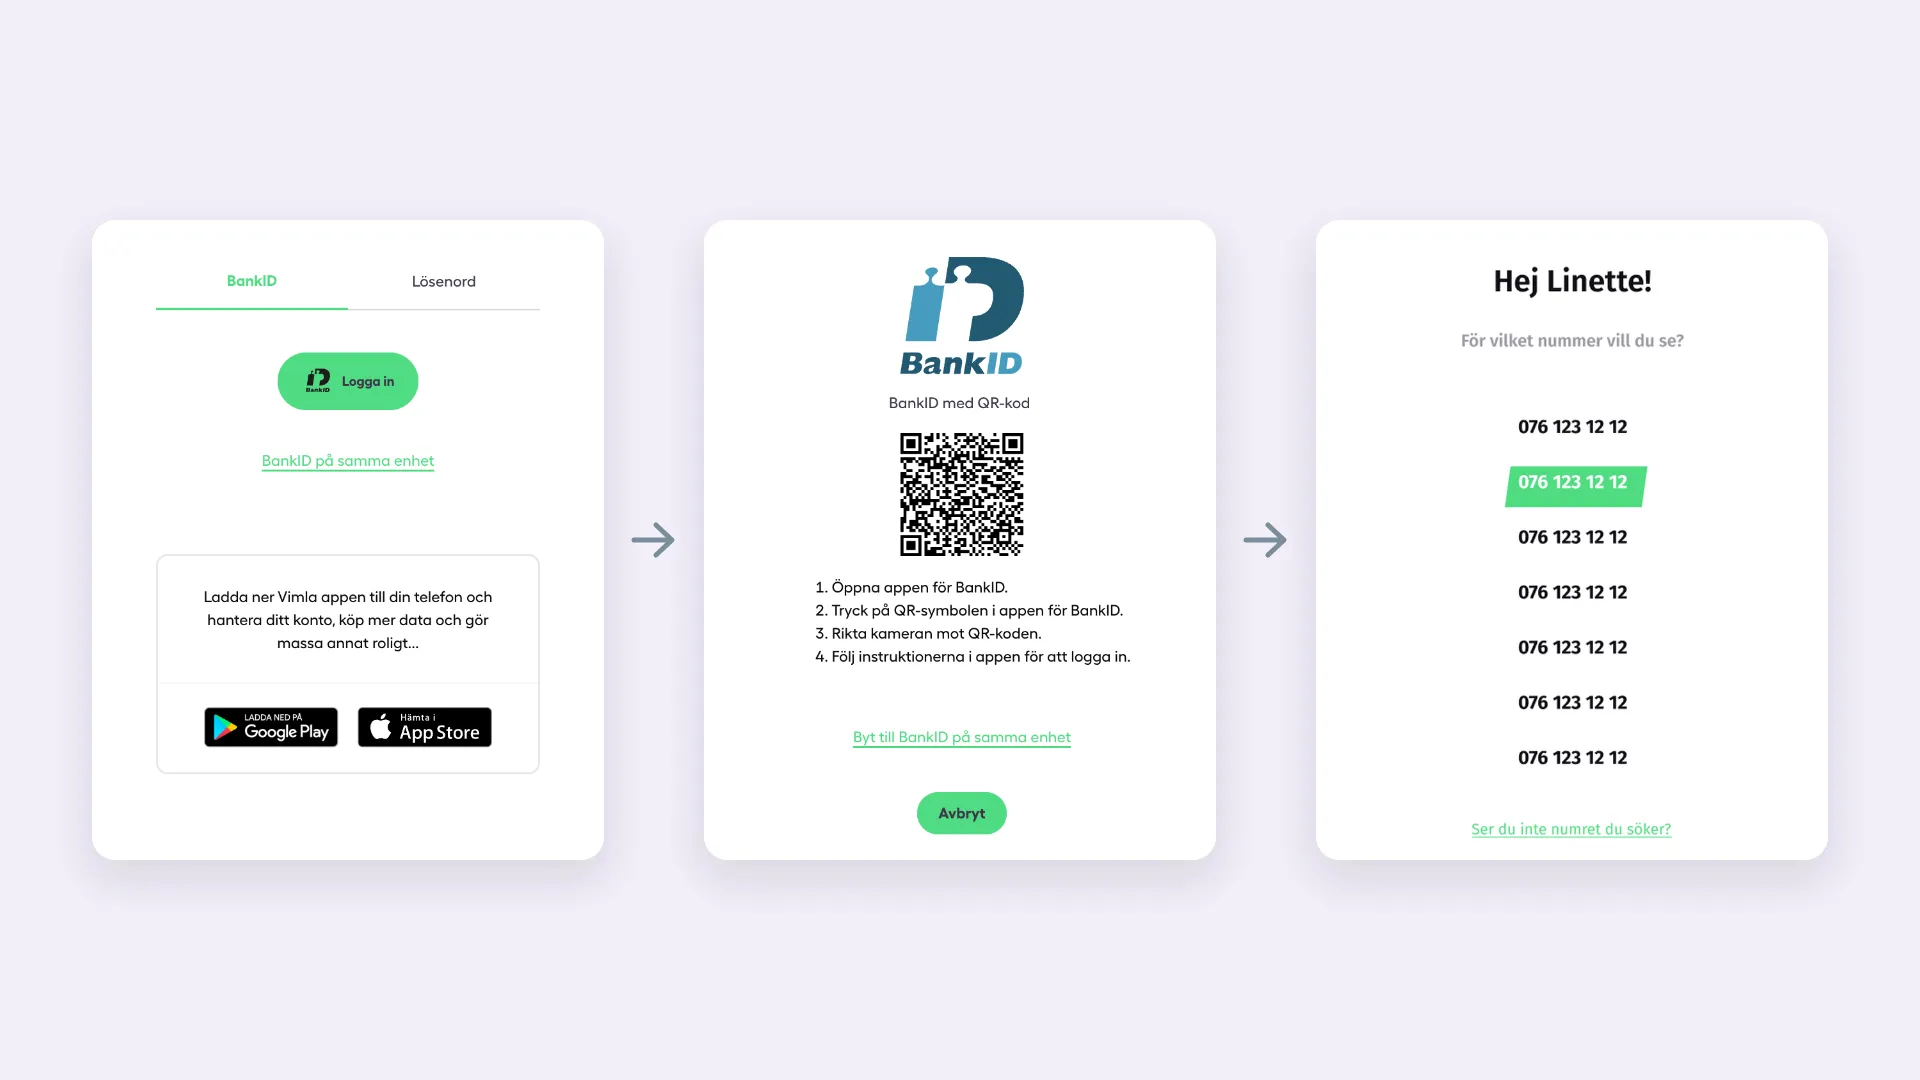
I worked from the architect’s specification and BankID’s documentation, designed the login flows and validated them with the product owner. A backend developer built mock BankID tools for the development environment.
Across the stack
I built the React and React Native clients on web and app, and the Node.js backend that calls BankID and handles the tokens. The scope included a subscription picker, so a customer logs in once and switches between their subscriptions.
Mismatched sessions
The hardest part was session handling. BankID’s token expires sooner than the subscription’s, so I designed and built for states where the subscription session is still valid but the BankID session has expired, and switching subscription has to be disabled.
The outcome
BankID became the login method most customers prefer, and they reach all their subscriptions from one login.